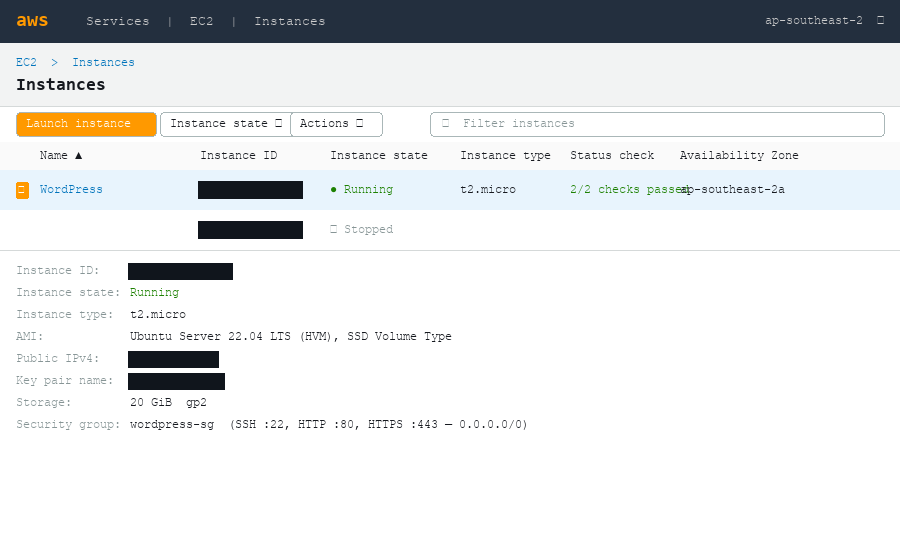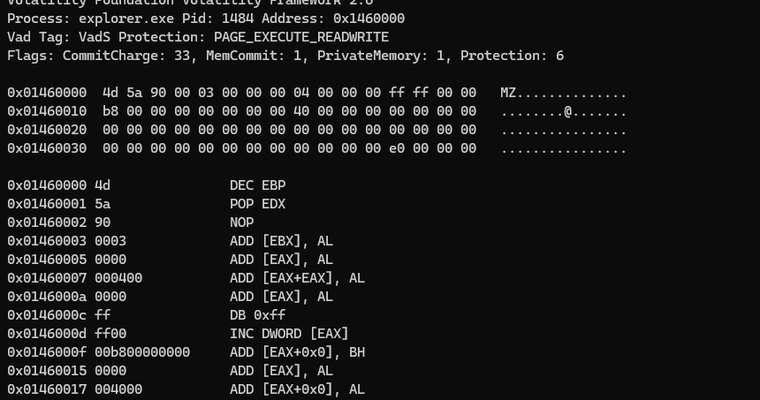
Memory forensics investigation
Analysed a Cridex malware memory sample. Found code injected into explorer.exe and a disguised Run key used for persistence.
- Volatility
- NIST SP 800-86
I study how AI systems break and how to protect them. I also explain security in plain language.
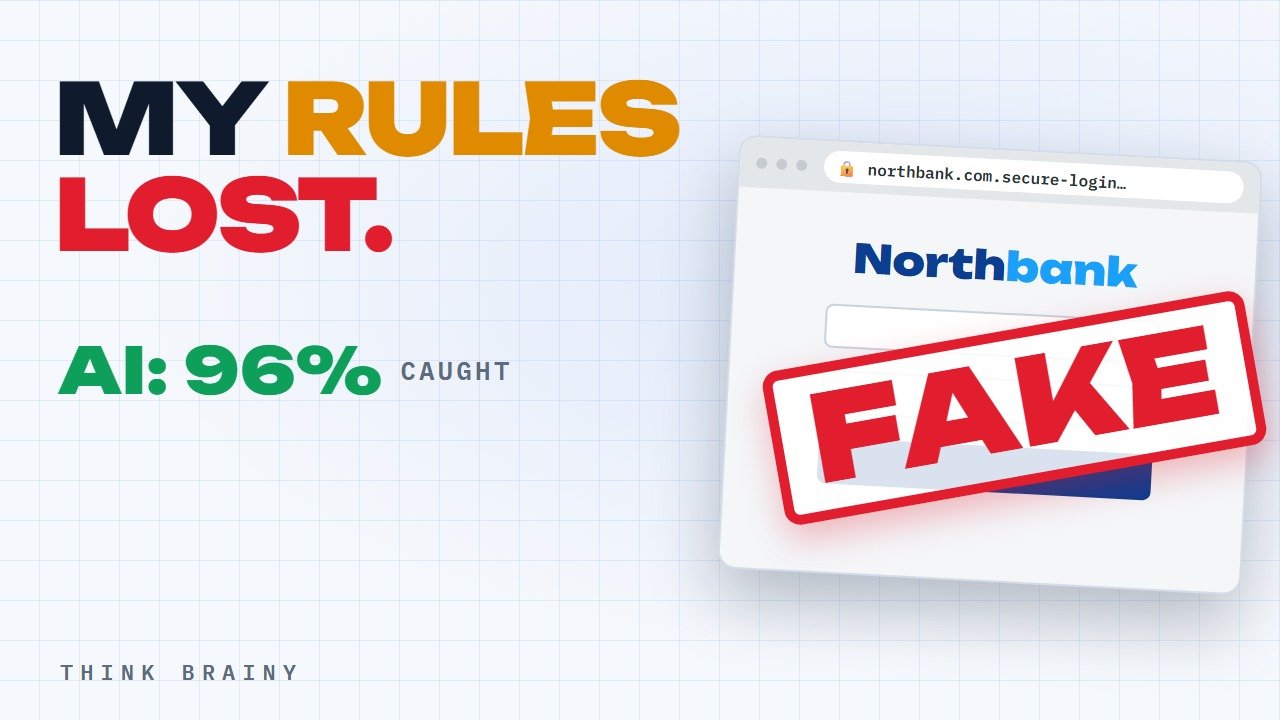
I tried two ways on 11,055 real websites: my own rules, then AI.
Watch the video →Hands-on projects from my studies, with the tools I used.
Analysed a Cridex malware memory sample. Found code injected into explorer.exe and a disguised Run key used for persistence.
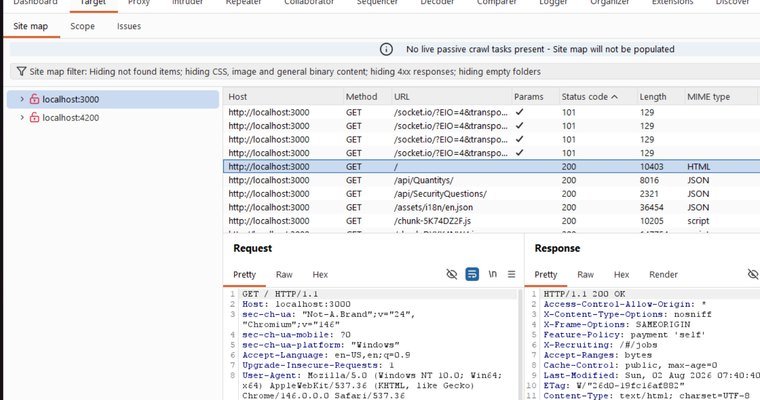
Tested OWASP Juice Shop. Intercepted login traffic, mapped the site and identified issues such as a missing Content Security Policy.
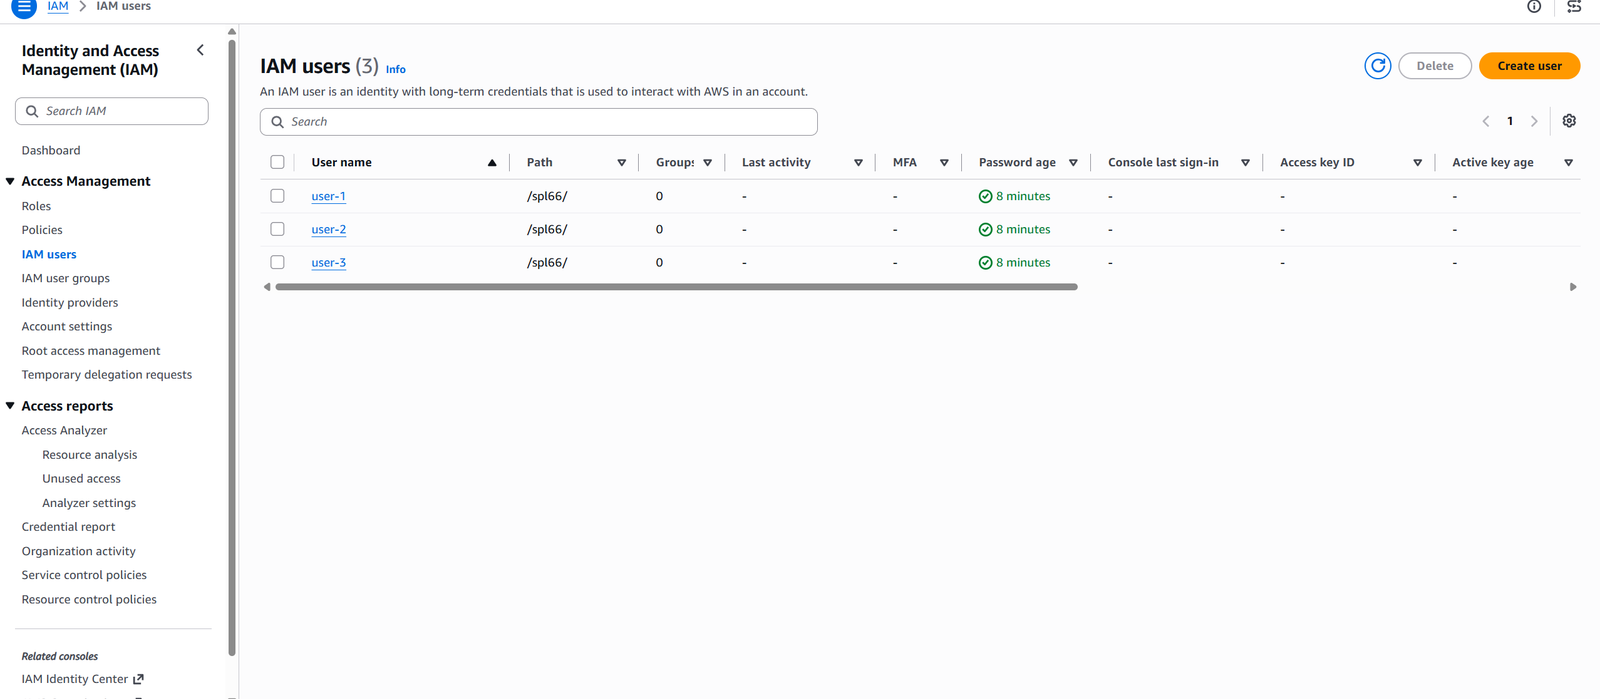
Reviewed IAM users, groups and policies, assigned access by business need, and tested it by signing in as each user.
I started in IT support, managing user access and fixing everyday IT problems. I then moved into security and research.
Master of ICT Research, 2026 to present
Bachelor of Information Technology, completed 2026
Technical Support Specialist, Jan 2025 to Jan 2026
AI and security. I study how AI systems break and how to protect them, and I do hands-on security work such as memory forensics, web application testing and access control.
I started in IT support, managing user access and fixing everyday IT problems. I then moved into security and research, and I am now completing a Master of ICT Research at Melbourne Institute of Technology.
I am based in Sydney, and I am open to work across Australia.
Yes. I am open to roles and research work. The quickest way to reach me is the contact form.
Yes. The Projects page explains what I did and the tools I used, and the blog has step-by-step guides.
Use the contact form or message me on LinkedIn.
For roles, research or a question about AI and security, send me a message.