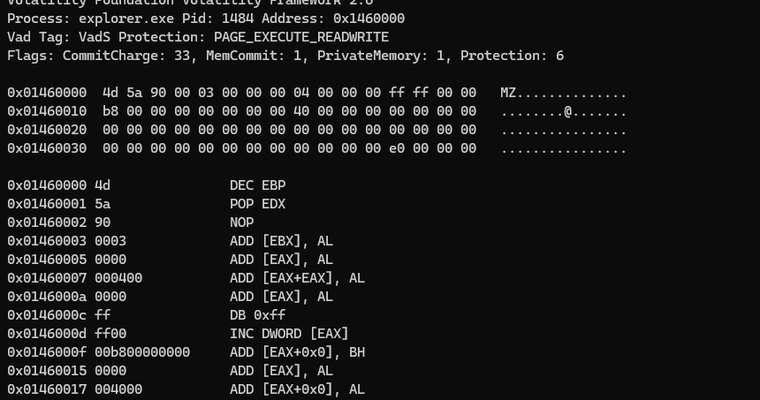
Memory forensics investigation
MN624 Digital Forensics, 2026. I owned the memory forensics task in a team of four.
I analysed a Cridex malware memory sample with Volatility. I found code injected into explorer.exe and a disguised Run key used for persistence, then reported the evidence following NIST SP 800-86.